7 Benefits of Cloud Computing for Modern Businesses
A company that adjusts technology as quickly as customer demand can respond to change, one benefit of cloud computing. For U.S. businesses, the choice can affect spending, teamwork, and how quickly people can test new ideas. A small shop may want a better way to handle holiday orders. A large organization may need teams in many locations to use the same tools.
Cloud services can help with those needs, but results depend on the workload and how well the business manages it. A service that suits one team may not fit an older application or sensitive information. This article pairs practical examples with the trade-offs you should weigh before making a change.
The best starting point is to match each expected benefit to a real business need.
Key Takeaways
- Cloud resources can help teams start projects without buying every server.
- Capacity can rise or fall as workload demand changes.
- Pay-as-you-go pricing does not guarantee a lower bill.
- Provider and customer security duties must both be managed.
- Backups need tested recovery plans to protect business operations.
- Measure cloud use against a business result, not just a bill.
What Cloud Computing Means and How It Works
A cloud service lets a business use computing resources over a network instead of owning and operating every underlying server. Cloud computing can provide compute power, storage, databases, and software, usually through the internet. The team selects a service and uses it when needed.
The five characteristics of cloud computing are on-demand self-service, broad network access, resource pooling, rapid elasticity, and measured service. The National Institute of Standards and Technology defines these traits in its cloud computing definition.
Cloud services change who operates the underlying technology, not whether physical hardware exists.
Here is what those five characteristics mean in daily work:
- On-demand self-service lets an authorized user start resources without asking the provider to set up each request.
- Broad network access makes services available over networks from supported computers, phones, or other devices.
- Resource pooling lets a provider serve many customers with shared infrastructure and assigned resources.
- Rapid elasticity means capacity can grow or shrink as workload demand changes.
- Measured service tracks use, such as storage or processing time, for monitoring or billing.
For example, a sales team may open browser-based software and shared files from several offices. The team uses the service, while the provider runs the underlying systems. That arrangement can spare the business from setting up a local server room for every new tool.
Elasticity is the ability to increase or decrease cloud capacity as workload demand changes. The provider still relies on physical data centers, servers, and storage to deliver services. An internet connection and account permissions also shape what users can reach.
The practical difference is who operates the underlying technology, not whether physical hardware exists. A business should still know which systems hold its information and who can manage them.

Which Cloud Deployment Model Fits Your Workloads?
The right deployment model depends on where a workload must run and how much control its owner needs. Public cloud suits many shared services, while private and combined environments can meet tighter control needs. The choice should reflect the application, data, and operating rules.
Map each workload’s location and control needs before choosing its environment. The four commonly discussed models differ in where resources run and how teams manage them.
| Model | Where resources run | Control profile | Common fit |
|---|---|---|---|
| Public cloud | Provider data centers | Provider operates shared infrastructure | Variable or general workloads |
| Private cloud | Dedicated environment | Greater control over access and setup | Tightly controlled workloads |
| Hybrid cloud | Private and public environments | Workloads split across connected settings | Existing systems plus public services |
| Hybrid multicloud | Private setting and multiple providers | Control spans several environments | Workloads with varied provider needs |
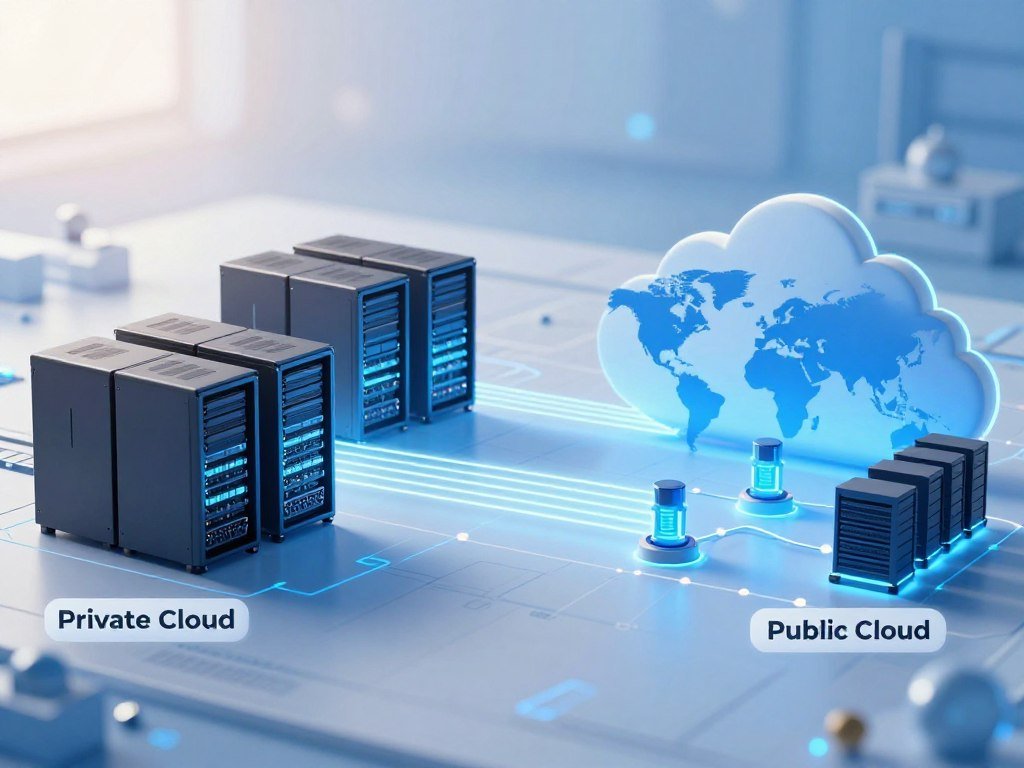
A public cloud provider operates the shared infrastructure, while customers choose and configure their services. A private cloud dedicates an environment to one organization. It may run at a business site or through a provider, depending on the arrangement.
Hybrid cloud connects private and public environments so a business can place different workloads where they fit. A company may keep sensitive or tightly controlled workloads in a private environment, then use public cloud for other tasks.
Multicloud means using services from more than one provider. It does not automatically mean hybrid cloud, since an organization can use several public providers without a private environment. Hybrid multicloud combines both ideas.
In 2026, 73% of surveyed organizations operated hybrid cloud environments, and 14% used multicloud without private cloud. Those figures describe different arrangements, not a rule that every business should follow.
Cloud providers offer different services, and the same organization may use more than one environment over time. For example, a regulated business could keep a tightly controlled database private while testing a customer-facing application in public cloud.
Map the workload’s requirements before choosing a model, rather than moving every application into the same environment. Check where data must stay, which teams need access, and how the workload connects to existing systems.
1. Benefits of Cloud Computing: Faster Launches and Greater Agility
A development team can start testing a cloud-hosted feature as soon as it has the resources, rather than waiting for a hardware purchase and installation. Rapid access to compute, storage, and development platforms can shorten the time between an idea and a working application.
On-demand provisioning can remove hardware setup as a project’s first delay. A retailer, for example, can test a new checkout feature on cloud servers before deciding whether it belongs in the full online store.
That approach gives a team a place to try a small change without buying and installing equipment first. If the feature fails, the team can learn from the test before committing more time. If it works, developers can prepare it for release.
DevOps practices bring development and operations work closer together. Continuous integration and continuous delivery, often shortened to CI/CD, let teams build, test, and release changes in smaller steps. Cloud services can provide test environments for those steps.
What are three benefits of cloud computing? Teams can test product features sooner, handle seasonal demand with more capacity, and share project files across locations. Each example has a different business goal, even when the same service supports it.
A product team might test a sign-up change with a small group before a launch. A retailer might add capacity during a holiday sales spike. A distributed project team might work from shared documents instead of emailing separate copies.
These examples show why businesses use cloud computing: they can get resources when a project needs them. The benefit matters most when it removes a real delay or helps a team learn sooner. Fast provisioning alone does not make a weak idea worthwhile.
A short trial workload is a sensible way to test whether faster provisioning improves a real launch. Choose one small feature and compare its test schedule with the team’s usual process.
2. Scale Capacity Up or Down With Demand
A business with sharp seasonal demand can add capacity for its busy period and reduce it when traffic subsides. Elasticity lets computing resources follow demand, instead of forcing a team to keep peak capacity all year.
Scaling out adds instances, while scaling up increases the capacity of an existing instance. An instance is a running virtual server or other computing resource. The choice depends on how the application handles work and where its limits appear.
A retailer may add server instances when holiday orders surge. When visits fall, it can remove some of those instances. This is horizontal scaling, also called scaling out, because the service uses more instances to share the work.
Vertical scaling, or scaling up, gives one instance more capacity, such as more memory or processing power. A database may need that approach if one large task strains its current setup. A later reduction can return the instance to a smaller size.
Automatic scaling can make these changes in response to measured use. Kubernetes can orchestrate containerized workloads across environments, helping teams manage how containers run and where they receive resources.
Automatic rules need sensible thresholds and active monitoring. A rule that reacts to every brief traffic bump may add more capacity than the workload needs. A threshold set too high may leave users waiting while the system catches up.
For example, an online ticket shop could set a capacity limit before a concert sale. The limit helps avoid uncontrolled growth, while a usage alert tells the team when demand nears the threshold. The same idea can suit a small store or a large organization.
Growth planning also includes people and operations, not only servers. A local food business, for instance, needs to match production capacity with demand before expanding. Planning for business growth helps frame that wider question.
Set scaling limits and alerts before an automated rule can expand a workload without oversight. Review the rules after a busy period, when real traffic can show whether they worked as intended.
3. Pay for Cloud Resources Without Buying Every Server
Cloud computing can reduce the need to buy for peak capacity, but unused resources and overlooked charges can erase the savings. Consumption-based pricing shifts spending from upfront hardware purchases to ongoing charges for services used.
The four primary cloud bill components are compute, storage, networking, and licensing. Each one can rise for a different reason, so a low charge in one area does not prove the total cost is low.
| Purchasing model | Commitment | Typical price behavior | Suitable workload |
|---|---|---|---|
| On-demand | No long-term commitment | Flexible use, often higher unit rate | Short tests or uncertain demand |
| Committed-use | Commit to a term or usage level | Lower unit rates in return for commitment | Steady, known workloads |
| Spot | Use spare provider capacity | Typically cheaper, but can be interrupted | Work that can pause or restart |
A virtual machine, or VM, is a software-based computer that runs on a physical server. AWS, Microsoft Azure, and Google Cloud offer on-demand, committed-use, and spot VM purchasing models. Exact terms depend on the provider, service, region, and commitment.
Committed use generally trades a commitment for lower unit rates. Spot capacity is typically cheaper because it uses spare capacity, but the provider can interrupt it. A job that must run without interruption may not suit that trade-off.
Networking charges can also surprise a team. Providers typically charge little or nothing for inbound network traffic, while moving data out of a provider’s network can bring egress fees. Large exports, backups, or transfers between regions can add to the bill.
A startup may keep an early test on-demand because its usage is hard to predict. A stable nightly task may fit a committed plan, while a batch job that can restart may work with spot capacity. The right choice follows the job, not a blanket rule.
Consumption pricing can support cost savings when teams match resources to actual use. It can also hide waste when forgotten systems keep running or when people choose a plan before they know the workload’s pattern.
Check actual usage and data-transfer patterns before committing to a pricing plan. A bill review should include the work each resource supports, not just its monthly total.
4. Give Teams Access to Files and Tools Across Locations
A field employee can pull up the same authorized customer record as a colleague at headquarters, without carrying the office server along. Shared access to cloud applications and files can help people work across locations.
Users still need a working internet connection and suitable permissions. Cloud access does not mean every employee should see every file, or that a tool will work when a device cannot connect.
Access work resources beyond the office
Authorized employees can open work files and applications from internet-connected devices, including while traveling. A manager might review a schedule from a phone, while an office teammate updates it from a laptop.
Cloud services can help organizations support teams spread across cities or regions. Google Cloud offers 43 regions and 130 zones across six continents. Its network provides connectivity across more than 200 countries and territories.
Cloud storage benefits for shared work
Shared documents can give a team one central version to edit instead of many emailed copies. Benefits of cloud storage include access across devices and simpler file sharing, when the service and permissions fit the job.
For example, a sales team traveling to separate customer visits can update the same customer record. The next colleague can see the latest notes, rather than relying on an old attachment. That can reduce confusion about which file holds the current details.
Shared access works best when each person can find the material needed for a task. A project folder might be open to the project team, while payroll records remain limited to staff who handle pay. The setup should follow actual roles.
Cloud services do not remove every barrier to teamwork. A weak connection can block access, and a badly chosen sharing setting can expose information. Teams should know how to work when a device loses its connection.
Set access permissions around job roles so convenience does not turn into broad access to sensitive files. Review sharing rights when staff change roles or leave the business.
5. Strengthen Security With Clear Shared Responsibilities
A provider can secure the infrastructure it operates, but a customer can still expose data through a weak identity policy or a misconfigured service. Shared responsibility means each party has security work to do.
Customers remain responsible for their data, identities, access policies, and service configuration. AWS describes provider duties as security “of” the cloud and customer duties as security “in” the cloud.
What the provider protects
The provider secures its facilities, physical hardware, host operating system, and virtualization layer. Those duties cover the underlying infrastructure that delivers a cloud service, rather than every setting a customer chooses.
What the customer must secure
Customers manage information, accounts, permissions, and service settings. Microsoft states that customers own their data and identities across deployment types. The customer’s tasks can differ by the service model.
| Service model | Provider manages | Customer manages | Customer responsibility that remains |
|---|---|---|---|
| IaaS | Facilities, hardware, virtualization | Operating system, applications, data | Accounts, access, configuration |
| PaaS | Infrastructure, operating system, runtime | Applications and data | Accounts, permissions, service settings |
| SaaS | Application and underlying platform | Data, accounts, sharing settings | Identity and appropriate sharing |
In infrastructure as a service, or IaaS, customers manage the operating system, applications, and data. In platform as a service, or PaaS, the provider also manages the operating system and runtime. In software as a service, or SaaS, customers still manage data, accounts, and sharing settings.
Common security risks include misconfiguration, exposed credentials, and access that is broader than a person’s job requires. For example, a public file setting can expose a private document, while a stolen password can give an attacker a valid account.
Useful controls include encryption, multifactor authentication, least privilege, logging, and zero trust. Multifactor authentication asks users for more than a password. Least privilege limits each account to the access needed for its work.
Zero trust checks access rather than assuming that a user or device is safe because it is inside a network. Logging can help teams spot unusual activity and trace what happened during an incident. The SEI cloud security guidance describes practical ways to manage these duties.
Security responsibilities can vary by provider and change when a customer enables a new service. Review the responsibility details whenever you enable a new cloud service, because the division of duties can change.
6. Recover Data and Restore Operations After Disruption
A cloud backup can preserve a copy of business data when a local device or server fails. Off-site copies can help a business recover after hardware failure, malware, or another disruption.
A backup protects copies of data, while disaster recovery restores services and business operations. A stored copy is useful, but it does not explain how staff will bring an application back online.
Backups protect data; recovery plans restore services
A backup can hold a customer database away from the local server that normally runs it. If that server fails, a business may use the copy to restore records on working equipment or a cloud service.
For example, a small company could lose its local database after a storage device breaks. A recent cloud backup may let staff restore customer records, then reconnect the application used to view and update them.
That work can include more than restoring files. Staff may need access to the application, related systems, and instructions for serving customers during the outage. Each part belongs in the recovery plan.
Recovery targets make plans testable
A recovery point objective, or RPO, sets how much data loss an organization can tolerate. A recovery time objective, or RTO, sets the time allowed to restore a service. Both targets turn broad hopes into clear goals.
If a business sets an RPO of one day, its plan must address how much recent work it can afford to lose. An RTO helps teams judge how quickly a key application must return. The targets should reflect the cost of downtime for that service.
Backups can fail, miss needed files, or prove hard to restore. A test can show whether the copy opens and whether the recovered information works in the business application. Keep a record of what the test found.
A backup is not a recovery plan until restoration has been tested. Run a restore test on a schedule the business can sustain, and confirm that the recovered files are usable.
7. Reach Modern Tools Without Building Every Platform
A small team can test an analytics or AI service without first building a specialized computing platform of its own. Managed tools can give businesses access to new capabilities while providers handle parts of the service.
Cloud services let teams try tools before they commit to a large in-house platform. The right choice still depends on the work, the data, and the skills available to manage results.
AI and analytics for new capabilities
Cloud providers offer generative AI, machine learning, and analytics services. A company might test an AI tool on a limited support task, or use analytics to find patterns in sales information before funding a larger system.
In 2026, generative AI was the third most widely used public cloud service, at 58%, up from 50% in 2025. That wider use makes clear rules for testing and oversight more important.
Large enterprises are setting up formal oversight as AI use grows. In 2026, 85% reported a dedicated team or senior leader responsible for AI oversight. Smaller organizations can assign a clear owner, even without a separate department.
AI services can help a team explore a new product idea with less early investment. A business could also consider a focused software tool instead of building every feature itself. These B2B SaaS startup ideas show examples of cloud-based software.
Teams testing new products can also use existing tools to learn what customers need before building a larger platform. AI and SaaS startup ideas include lean ways to test a service.
Efficiency and sustainability require active choices
Provider-managed services can reduce some maintenance work for a customer team. Providers may also use data centers efficiently by serving many customers on shared systems. Those features do not prove that every cloud workload has a lower environmental impact.
Environmental impact depends on the workload and energy choices, not on the word “cloud” alone. A business should consider how much computing a task needs and how its provider powers the service.
AI oversight matters because a tool may handle business information or shape decisions. Teams should set rules for approved uses, review outputs, and decide who can enter sensitive data. A tool that helps with a draft may not suit private customer records.
Assign an owner to review AI use before sensitive business data enters a new tool. That person can set clear limits and help teams know which tasks are approved.
What Are the Main Drawbacks of Cloud Computing?
Cloud services transfer some operational work to a provider, but they do not remove every business risk. Cloud computing’s pros and cons depend on the workload, connectivity, and the customer’s ability to manage the environment.
Ten common disadvantages affect access, control, security, compliance, and spending. A service may work well for one task and still create problems for another.
- Internet dependence: users may lose access when their connection fails.
- Provider outages: a provider’s service may become unavailable.
- Vendor lock-in: moving an application or its data can be hard.
- Less control over underlying infrastructure: customers cannot manage every physical layer.
- Data privacy exposure: sensitive information can be mishandled or exposed.
- Misconfiguration risk: incorrect settings can leave services open.
- Credential theft: stolen account details can enable unauthorized access.
- Compliance or data-residency constraints: rules may limit where information can sit.
- Integration and migration complexity: cloud services may not fit older systems easily.
- Unexpected spending: unmonitored use can raise charges beyond expectations.
Internet dependence can affect a team even when its application and data remain available at the provider. A sales employee without a connection may be unable to open the customer record needed for a visit.
Lock-in can grow when an application depends on provider-specific tools or data formats. An open, portable architecture can reduce that risk, but it may add integration work and require more technical skills.
Security and privacy concerns also depend on how the customer sets up and uses the service. A business must consider its own rules, contracts, and legal duties before moving information into a cloud environment.
These drawbacks do not mean that every cloud service is a poor fit. They show why a workload, its users, and its support needs should be considered together. A task that must keep running through a network outage may need another way to operate.
Keep a local or alternate access plan for work that cannot pause when connectivity fails. Choose a practical backup process for the people who need to keep serving customers.
How Can Businesses Control Cloud Spending and Measure Value?
A cloud cost is useful to a business only when its owner can connect the spending to a service or outcome. Unit economics means tracking the cost of a service alongside the result it supports.
A cloud bill alone shows spending, not whether the business gained value. A team might track cost per customer account, order, or completed task, then compare the figure with service results.
Track cost by service and business unit
Unit economics links cloud consumption to a business outcome. It helps a manager ask whether a service costs more as it grows, or whether better results justify the added use.
In 2026, 49% of organizations used unit economics to measure cost per service and link cloud use to business outcomes, up from 40% in 2025. In the same year, 64% relied on value delivered to business units as their top cloud-progress metric, 12 percentage points above 2025.
Those measures can help teams compare spending with what a service does. A customer support tool might be measured against resolved cases, while an online store might track service cost per completed order.
Make ownership part of cloud governance
A cloud center of excellence can set shared practices and help teams make consistent choices. A FinOps team focuses on the cloud cost management practice, connecting finance, technology, and business owners.
In 2026, 71% of organizations had a cloud center of excellence or equivalent, and 63% had a FinOps team. Estimated wasted IaaS and PaaS spending was 29%, reversing a five-year downward trend.
A governance routine can make spending easier to understand without turning every purchase into a long approval process. Assigning owners gives teams a clear person to ask when usage changes or a service no longer supports its goal.
- Assign a spend owner to each service or business unit.
- Review usage against the business outcomes it supports.
- Remove resources that no longer serve an active need.
- Set alerts for unusual consumption.
The Flexera 2026 State of the Cloud survey included 753 technical professionals and executive leaders worldwide and was conducted in winter 2025. Its findings reflect reported practices, while each organization still needs measures that match its own services.
Review cost and value together at a regular cadence so a cheaper workload is not mistaken for a better business result. A falling bill means little if a key service also becomes less useful.
How to Plan a Cloud Adoption That Fits Your Business
Start by identifying a business problem and the workload most suitable for addressing it, rather than beginning with a provider’s product catalog. A phased plan can help you test a change before it affects more business operations.
Do not move an entire application portfolio before testing a representative workload. Some older applications have dependencies that make them poor first candidates for cloud services.
- Audit workloads and requirements.
- Choose a provider and services that fit those needs.
- Migrate a limited workload in phases.
- Train users and evaluate results.
Start the audit by listing the applications, data, and systems each workload depends on. A legacy application may rely on a local database or a device that cannot move with it. Those links can affect timing and cost.
Choose a workload with a clear business need and a manageable scope. A limited pilot can show how users respond and whether the chosen service works with nearby systems. It also gives the team a chance to learn before wider adoption.
Before choosing cloud-based services, compare their features with the needs uncovered in the audit. Ask which teams will manage the service and how information will move between it and existing applications.
A service-level agreement, or SLA, defines the service and expected performance level. Review SLA terms for latency, data availability, system uptime, and unplanned downtime. These details help clarify what the service promises and where its limits sit.
Move in phases so a problem with one workload does not disrupt every operation at once. Train users before each change, then gather feedback from the people who rely on the application each day.
Measure results against the business goal set at the start. A rollout may meet its technical target but still fail to improve the work that matters to customers or staff.
Set a success measure and a rollback plan before the first production workload moves. Agree on who can pause the change if the application does not behave as expected.
Test a representative workload before moving more applications, and decide in advance how you will reverse the change.
Conclusion
Cloud computing is most useful when its capabilities solve a defined business problem. It can support agility, access to modern tools, and business continuity when workload placement, security duties, and spending receive active attention.
You do not need to move every system to see whether the approach fits. Select one workload, write down its business goal, and choose a measurable outcome before evaluating services.
Choose one workload and document the outcome it needs to deliver before deciding how to move it.
FAQ
What are cloud computing risks?
Cloud computing risks include connectivity outages, vendor lock-in, misconfiguration, privacy exposure, and unexpected spending. Their effect depends on the workload and the controls a customer uses. A field team may feel a brief internet outage more than a back-office group. A business can reduce avoidable risk by limiting access, watching use, and planning how users will work if a key service becomes unavailable.
What are the 5 disadvantages of cloud computing?
Five common disadvantages are internet dependence, provider outages, vendor lock-in, reduced control over infrastructure, and security or privacy exposure. They do not affect every service equally. A workload that needs physical control may be a poor fit, while a task that can pause during an outage may tolerate network dependence. Consider how each issue affects the people and systems that rely on the service.
Can hackers get into your cloud?
Yes, hackers can get into cloud accounts through stolen credentials or misconfigured services. A provider’s infrastructure protection cannot prevent every customer-side mistake. Multifactor authentication makes a stolen password less useful, while least privilege limits what an account can reach. Monitoring can also help a team spot unusual sign-ins or activity before an intruder causes wider harm.
What should not be stored on the cloud?
No single category of information is always barred from cloud storage. Do not put information in a service that fails your organization’s legal, contract, or security requirements. For example, a service may not meet a rule about where records must stay or who may access them. Check the service settings and your organization’s data rules before storing sensitive material there.
Which is the safest cloud service?
No provider is automatically safest for every workload. Compare the controls a service offers, its compliance support, data location, identity tools, and the customer’s configuration duties. A service with strong account controls can still expose information if a customer shares files too broadly. Choose the option that matches the workload’s requirements and the team’s ability to manage its settings.
About The Author